The challenges of the GDPR
The entry into application of the GDPR marked an unprecedented awareness of data protection issues. This logically resulted in a considerable increase in complaints addressed to the CNIL. A new record for the number of complaints received was thus reached.
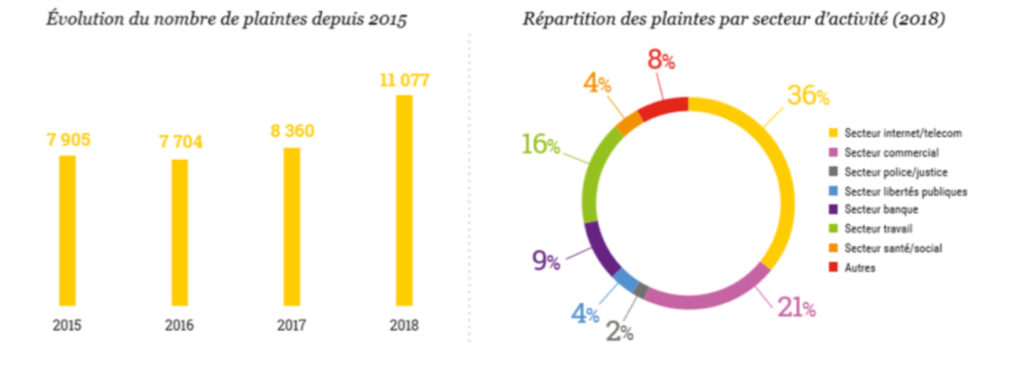 Sources: CNIL 2018 activity report
As a reminder, the GDPR aims to protect citizens against malicious use of their personal data.
Thus, organizations have more responsibilities. They must now ensure optimal data protection and be able to demonstrate this protection (documentation).
The consecration of the DPO
It is in this context that the GDPR established the DPO, the designation of which is obligatory in certain cases.
Indeed, the DPO must be designated in the organizations:
- which are “public authorities or public bodies, with the exception of courts acting in the exercise of their jurisdictional function” (including private law bodies in charge of a mission of public interest or exercising prerogatives of public power)
- whose basic activities consist of “processing operations which, due to their nature, their scope and/or their purposes, require regular and systematic monitoring on a large scale of the persons concerned”
- whose basic activities consist of large-scale processing of categories of sensitive data or data relating to offenses or convictions.
What is its function?
It guarantees that your company complies with its new obligations. Its main mission is to advise, inform and make recommendations to those responsible for processing information.
Why certification?
Certification allows people to demonstrate that they meet the delegate’s skills and know-how requirements provided for by the regulation. The delegate must indeed have specialist knowledge of data protection law and practices.
The CNIL adopted two standards on September 20, 2018:
- certification framework setting the requirements to be a candidate for certification and the list of 17 skills and know-how;
- approval framework setting the criteria applicable to certification bodies.
It is in this context that AFNOR Certification has become the first certification body approved by the CNIL to certify the skills of DPOs.
The certificate constitutes a vector of confidence both for the organization using these certified people but also for its customers, suppliers, employees or agents.
In conclusion, certification provides proof of the skills and know-how of the DPO according to the CNIL standards. It also allows, for client companies, to reassure their clients regarding the protection of their personal data.
A certification acquired by our firm
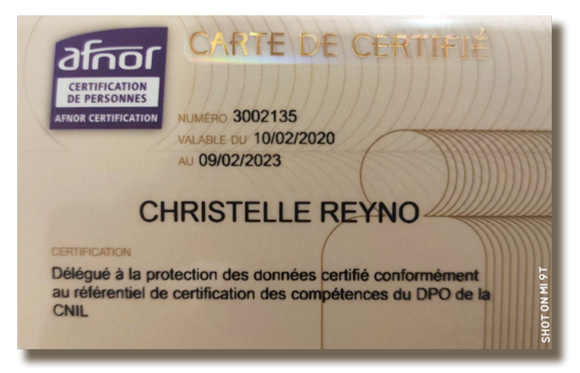
Maître Christelle REYNO was certified by AFNOR on February 10, 2020 and holds certificate no. 3002135.
Article published on May 2, 2020. Its content reflects the context of its publication.
A question about your situation? Contact the firm ↗